Cybersecurity Awareness Month continues where we will share tips on how to make life difficult for cybercriminals. This week we will investigate real cybercriminal, Dariy Pankov.
Dariy Pankov
Alias: dpxaker Weakness: Long, unique passwords
Dariy Pankov, known among hackers as “dpxaker,” paid for his lavish lifestyle by selling password-cracking software to criminals for just $250 – no subscription required. Powered by his program, hackers don’t have to sit in a dark room guessing passwords one at a time – dpxaker’s software and AI tests thousands of password combinations every second. He has a soft spot for pet names and birthdays and he really loves short passwords and reused passwords!
What You Can Do…
Make dpxaker’s life more difficult by creating strong password using the following guidelines:
Every password should be at least 16 characters long
Every password needs to be unique to the account
Every password should be a random mix of letters, numbers, and symbols
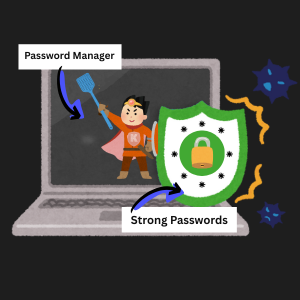
Use a password manager to create and store awesome passwords – they are safe, easy to use, and many are even free!
Remember…
An 8-character password can be cracked in seconds, no matter how many &s and !s you use. A complex 16-character password takes billions of years to crack – and hackers don’t have that kind of time
Subscribe to our Posts
Did you miss the latest announcement? Subscribe to receive our posts directly to your inbox!
Attributes: Portions of the written content from this blog was adapted from the Cybersecurity Awareness Month 2026 Toolkit published by Stay Safe Online National Cybersecurity Alliance. All images were designed by the IS Digital Solutions Administrator, Katrina Naoko Frank.
October is Cybersecurity Awareness Month and this month we’ll share tips on how to make life difficult for cybercriminals. Every week in October we will investigate real cybercriminals. While some of them have been arrested, more are following in their footsteps, and we want to give you tips to prevent them from striking again.
Alright, crew, we managed to scrape together the rap sheets on our three main players. They’ve left digital fingerprints all over the web. Here’s their files—study them and be prepared to make their lives difficult.
The Perps…
Dariy Pankov
Alias: dpxaker Weakness: Long, unique passwords
Dariy Pankov, known among hackers as “dpxaker,” paid for his lavish lifestyle by selling password-cracking software to criminals for just $250 – no subscription required. Powered by his program, hackers don’t have to sit in a dark room guessing passwords one at a time – dpxaker’s software and AI tests thousands of password combinations every second. He has a soft spot for pet names and birthdays and he really loves short passwords and reused passwords!
Giant Company
Location: Myanmar Strength: Large in numbers and excellent actors
Giant Company was one name for a massive scam operation targeting Americans. Almost 300 people were arrested in connection with the Giant Company, and 9 scam centers were disrupted as part of the crackdown. But Giant Company is a drop in an ocean of scams. Scammers and phishing attackers impersonate your bank, your boss, a delivery company, customer support, or even a family member.
Zestix
Government Identity: unknown Weakness: multifactor authentication (MFA)
Zestix invaded more than 50 multinational companies because a few people never turned on MFA. And if some of the biggest companies in the world can go down, it would be very easy for Zestix to hijack any account if it’s solely protect with a password. After swooping up stolen passwords on the Dark Web, criminals can break into many accounts that don’t enable MFA. They can also get their hands on passwords lost in data breaches and spray them all over the internet with automated software.
Subscribe to our Posts
Did you miss the latest announcement? Subscribe to receive our posts directly to your inbox!
Attributes: Portions of the written content from this blog was adapted from the Cybersecurity Awareness Month 2026 Toolkit published by Stay Safe Online National Cybersecurity Alliance. All images were designed by the IS Digital Solutions Administrator, Katrina Naoko Frank.
Get ready for those harmful hackers looking to get control of your accounts and add an extra layer of security by enabling multi-factor authentication.
Don’t get tricked and instead treat the security of all of your accounts equally. No matter how unimportant you think your account may be, hackers find value in everything.
Tips and Tricks
Password Creation
Hackers don’t hack in, they log in. Protect your passwords by making them complex and unique to each website.
The wilder, the better! A long, complex password is your first line of defense against hackers.
Memorizing and Storing Passwords
Do you find yourself clicking “forgot your password” again? Let a password manager remember it for you! By storing your login info in a vault, you’ll never forget it.
Give your memory a break and store multiple passwords in one password manager. Doing so is more secure and strengthens your defenses.
Subscribe to our Posts
Did you miss the latest announcement? Subscribe to receive our posts directly to your inbox!
Let’s avoid cybersecurity nightmares and prepare for this spooky season and beyond.
October is Cybersecurity Awareness Month where Information Services will share some tips to keep the phishing phantoms, horrid hackers, and the malicious malware away.
Subscribe to get your tips this month!
Subscribe to our Posts
Did you miss the latest IS announcement? Subscribe to receive our posts directly to your inbox!
Microsoft’s “Bookings with Me” (EDIT: also known as Personal Bookings) is now available as a tool for scheduling meetings, advising, and other one-on-one appointments. This is designed to integrate with your Outlook calendar and produce an easy-to-use website for people to book time on your calendar. If you’re previously familiar with Microsoft Bookings, Bookings with Me is a streamlined tool better designed for an individual user to set up quickly.
Want to Learn More About Microsoft Personal Bookings?
To kick off 2023, here are some new and some not so new IS resources that will come in handy throughout the quarter.
As always, if you need to connect, please feel free to send us an email at HelpDesk@kzoo.edu or stop by the Help Desk in the Upjohn Library Commons (located on the first floor to the right of the grand staircase). We’re open Monday – Friday: 8:00 a.m. – 5:00 p.m. with Student Computer Consultants available during some off hours.
Community Member Pages
Looking for resources depending on whether you’re a student, faculty, or staff member? If so, select the page that relates to you:
K faculty and staff are supposed to consult and partner with IS when considering any technology hardware; software; services; and any cloud or externally hosted systems. It’s true!
You can count on Information Services regularly performing upgrades and maintenance Thursday evenings from 5:00 p.m. to 7:00 p.m. During this time you can expect a brief VPN disruption.
Note: IS may not publish a weekly scheduled maintenance post if systems do not directly affect the campus community.
“A phishing email is an email that appears legitimate but is actually an attempt to get your personal information or steal your money” (Microsoft Support, Phishing and Suspicious Behaviour)
This IT Tip will share ways to identify suspicious emails and how to report a phishing case.
The email is from someone inside K or from a vendor, or partner and the email is very unusual or out of character.
You don’t have a business relationship nor any past communications with the sender.
The email is from someone outside of K and it’s not related to your job responsibilities.
The email is from a suspicious domain (like micorsoft-support.com)
To:
You were copied on an email sent to other people, but you don’t personally know the other people it was sent to.
The email was also sent to an unusual mix of people within your organization. For example, a group of people who last names start with the same letter.
Date and Subject:
The email was sent at an unusual time like 3 a.m. and not during regular business hours.
The subject line is irrelevant or does not match the message content.
The email message is a reply to something you never sent or requested.
Attachments
There is an attachment that you were not expecting or that does not make sense in relation to the email message.
There is an attachment with a possibly dangerous file type such as:
ZIP and RAR Files
DOC and DOCX
XLS, XLSX, XLSM
PDF
IMG, ISO, etc.
Hyperlinks
The biggest red flag – When you hover over the hyperlink to preview the URL and the link-to address is for a different website.
The email only has long hyperlinks with no other information.
The email has a hyperlink with a misspelling of a known website such as www.bankofarnerica.com (in this case the “m” is really two characters, “r” and “n.”
The sender asks you to click a link that seems odd and/or illogical.
Content
The email is out of the ordinary, has bad grammar, and/or spelling errors.
The sender asks you to click a link or open up an attachment that seems odd and/or illogical.
The sender asks you to click a link or open an attachment in order to gain something of value or avoid a negative consequence.
The email claims to have a compromising or embarrassing picture of yourself or someone you know.
Tips for checking a link without clicking on it
Simply hover over the link and look at the bottom left corner of your computer screen for the full URL the link actually goes to.
How to Report Phishing Attempts
The easiest way to report phishing emails is through the Report message option in Outlook which can be found in different locations depending whether you’re using Microsoft Office Outlook or Outlook.com.
With the suspicious message selected, do the following:
Choose Report message from the ribbon
Select Phishing.
This is the fastest way to report it and remove the message from your Inbox. It will also help Microsoft improve their filters so that you see fewer of these messages in the future.
Webmail at outlook.office.com
Select the check box next to the suspicious message in webmail. Select the arrow next to Junk, and then select Report phishing.
Note: If you’re using an email client other than Outlook, start a new email to phish@office365.microsoft.com and include the phishing email as an attachment. Please don’t forward the suspicious email; as it needs to be received as an attachment so the headers on the message can be examined.
Have Questions?
For more Microsoft documentation please visit the Phishing and Suspicious Behaviour page through Microsoft Support. Additionally, please feel free to email Help.Desk@kzoo.edu with more specific questions related to phishing emails.
Suggest an IT Tip
If you have a topic that you would like us to cover in the future, please complete the IT tip suggestion form or email, Katrina Frank at Katrina.Frank@kzoo.edu directly.
Visit the Wi-Fi troubleshooting page to assist you in resolving your issue. Please attempt all troubleshooting tips that apply to your circumstance before completing a report.
Due to the complexities of Wi-Fi-related problems, specific details are needed to help resolve Wi-Fi related issues. You must provide the following in order to submit a Wi-Fi Outage Report.
List of Required Information to Complete the Wi-Fi Outage Report Form
Name
The wireless network you were attempting to connect to
Screenshot of the error you encountered or the exact error message as displayed on your device
Note: A full screenshot of the error you are encountering is the most reliable way we can assist in resolving your issue
Date of occurrence
Time of occurrence
Location of occurrence
If this issue has happened elsewhere on campus. If so, the location(s) it has occurred
If the device was able to connect successfully in any other locations on campus. If so, the location(s) it has been successful
Type of device experiencing the issue –
Note: If you are using a device running on Android 10 or iOS 14 you will need to disable MAC randomization on your device first. See the Wi-Fi Troubleshooting section for instructions.