Cybersecurity Awareness Month: The Power of Pause & Review

Perp 2: Giant Company

Cybersecurity Awareness Month continues where we will share tips on how to make life difficult for cybercriminals. This week we will investigate real cybercriminals like Giant Company.

Location: Myanmar
Strength: Large in numbers and excellent actors

Giant Company was one name for a massive scam operation targeting Americans. Almost 300 people were arrested in connection with the Giant Company, and 9 scam centers were disrupted as part of the crackdown. But Giant Company is a drop in an ocean of scams. Scammers and phishing attackers impersonate your bank, your boss, a delivery company, customer support, or even a family member.
What You Can Do…

Understand that scammers and phishing attackers impersonate your bank, your boss, a delivery company, customer support, or even a family member. They want you to click their links, take their phone calls, open their DMs, respond to their “accidental” texts, and, eventually, send them your hard-earned money.

And now with AI, scammers can do more crime every day! These big scamming syndicates love to make you feel something and act fast.

Make entities like Giant Company’s life more difficult by using the following guidelines:

  • Be extremely suspicious of every unexpected inbound message, especially if it seems urgent
  • Take a few seconds (4-9 seconds) when reviewing all communication
  • Look out for urgency, like fear (“you just got hacked!”) and pressure (“you won an expensive grill!”)

Remember…

You don’t need to click. You don’t need to respond. You don’t need to answer the phone. You aren’t being rude. Their biggest enemy isn’t technology. It’s your skepticism.

Subscribe to our Posts

Did you miss the latest announcement? Subscribe to receive our posts directly to your inbox!

Attributes: Portions of the written content from this blog was adapted from the Cybersecurity Awareness Month 2026 Toolkit published by Stay Safe Online National Cybersecurity Alliance. All images were designed by the IS Digital Solutions Administrator, Katrina Naoko Frank.
Cybersecurity Awareness Month: Password Power

Perp 1: dpxaker

Cybersecurity Awareness Month continues where we will share tips on how to make life difficult for cybercriminals. This week we will investigate real cybercriminal, Dariy Pankov.

Alias: dpxaker
Weakness: Long, unique passwords

Dariy Pankov, known among hackers as “dpxaker,” paid for his lavish lifestyle by selling password-cracking software to criminals for just $250 – no subscription required. Powered by his program, hackers don’t have to sit in a dark room guessing passwords one at a time – dpxaker’s software and AI tests thousands of password combinations every second. He has a soft spot for pet names and birthdays and he really loves short passwords and reused passwords!

What You Can Do…

Make dpxaker’s life more difficult by creating strong password using the following guidelines:

  • Every password should be at least 16 characters long
  • Every password needs to be unique to the account
  • Every password should be a random mix of letters, numbers, and symbols
  • Use a password manager to create and store awesome passwords – they are safe, easy to
    use, and many are even free!

Remember…

An 8-character password can be cracked in seconds, no matter how many &s and !s you use. A complex 16-character password takes billions of years to crack – and hackers don’t have that kind of time

Subscribe to our Posts

Did you miss the latest announcement? Subscribe to receive our posts directly to your inbox!

Attributes: Portions of the written content from this blog was adapted from the Cybersecurity Awareness Month 2026 Toolkit published by Stay Safe Online National Cybersecurity Alliance. All images were designed by the IS Digital Solutions Administrator, Katrina Naoko Frank.
Cybersecurity Month – Make Life Difficult for Cybercriminals

cybercriminal failing to access a user's account after many attempts.

October is Cybersecurity Awareness Month and this month we’ll share tips on how to make life difficult for cybercriminals. Every week in October we will investigate real cybercriminals. While some of them have been arrested, more are following in their footsteps, and we want to give you tips to prevent them from striking again.

Alright, crew, we managed to scrape together the rap sheets on our three main players. They’ve left digital fingerprints all over the web. Here’s their files—study them and be prepared to make their lives difficult.

The Perps…

Alias: dpxaker
Weakness: Long, unique passwords

Dariy Pankov, known among hackers as “dpxaker,” paid for his lavish lifestyle by selling password-cracking software to criminals for just $250 – no subscription required. Powered by his program, hackers don’t have to sit in a dark room guessing passwords one at a time – dpxaker’s software and AI tests thousands of password combinations every second. He has a soft spot for pet names and birthdays and he really loves short passwords and reused passwords!

Location: Myanmar
Strength: Large in numbers and excellent actors

Giant Company was one name for a massive scam operation targeting Americans. Almost 300 people were arrested in connection with the Giant Company, and 9 scam centers were disrupted as part of the crackdown. But Giant Company is a drop in an ocean of scams. Scammers and phishing attackers impersonate your bank, your boss, a delivery company, customer support, or even a family member.

Government Identity: unknown
Weakness: multifactor authentication (MFA)

Zestix invaded more than 50 multinational companies because a few people never turned on MFA. And if some of the biggest companies in the world can go down, it would be very easy for Zestix to hijack any account if it’s solely protect with a password. After swooping up stolen passwords on the Dark Web, criminals can break into many accounts that don’t enable MFA. They can also get their hands on passwords lost in data breaches and spray them all over the internet with automated software.

Subscribe to our Posts

Did you miss the latest announcement? Subscribe to receive our posts directly to your inbox!

Attributes: Portions of the written content from this blog was adapted from the Cybersecurity Awareness Month 2026 Toolkit published by Stay Safe Online National Cybersecurity Alliance. All images were designed by the IS Digital Solutions Administrator, Katrina Naoko Frank.
Freeze Lifted – What You Should Know

happy illustrated character with two thumbs up signifying it's ok to edit WordPress.

Available Systems

We are happy to share that the content freeze for the Campus Web Infrastructure Modernization Project is now lifted!

Site Content Editors (SCEs) can now made edits to their department websites and the Hornet Hive Announcements as well as the Campus Event Calendar are available for submissions.

If you would like to report any website related issues you experience please complete the website issue/question report form.

For other questions related to this project please email wphelp@kzoo.edu.

New Process for Logging into Websites at K

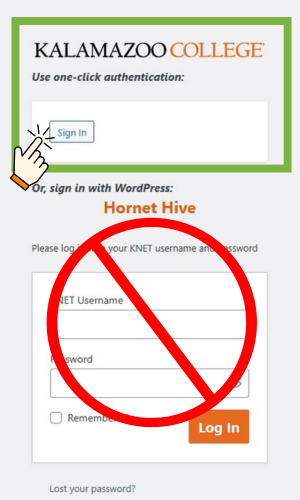
If you are prompted to log in to view a webpage:

Do

Select the Sign-In button to use the one-click authentication option

Don’t

Do not enter your KNET username and password to sign in with WordPress as this is only meant for WP admins.

Note: If you enter your KNET credentials as opposed to using the single sign-on option, you may be delayed in attempting to log in again. Please reach out to the Help Desk if you are unable to use single sign-on.

Reminder: Web Content Freeze Today!

WordPress, Hornet Hive, and Campus Event Calendar Out of Service

As part of the Campus Web Infrastructure Modernization Project, Kalamazoo College websites will be unavailable from noon today, August 19th to noon Thursday, August 20.

During this freeze period, any changes or updates made by Site Content Editors will be lost and have to be repeated after the freeze.

We also ask all members of the campus community to refrain from submitting Hornet Hive Announcements and Campus Event Calendar requests during this period. Any submissions made during the freeze period may not be processed and could be lost as we complete the migration. Also during this period, there may be brief moments of inaccessibility or strange formatting on our web site while the work progresses, though we expect this to be minimal.

Information Services will notify the campus community when the work is completed. We will also provide a form for reporting any website-related issues that may arise.

Cybersecurity Tip: Multifactor Authentication

a graphic representing three trick or treaters holding a shield that spells MFA.

Be Prepared…

Get ready for those harmful hackers looking to get control of your accounts and add an extra layer of security by enabling multi-factor authentication.

Hornet HQ Now Using Single Sign-On

As of today, the login to Hornet HQ will use will add Single Sign-on (SSO) and Multifactor Authentication (MFA) in the way already in use for Outlook email, Teams, VPN, and other services.

With this change, the existing parent proxy access to Hornet HQ will be retired.  Instructions for setup of authorized user access in the Payment Center are being provided to students (for parent/guardian) as well as to retirees (for spouse/partner).

What is changing? 

  • The login to Hornet HQ on February 14, 2025.
  • The username will need to be in the format of first.last@kzoo.edu (students: first.last99@kzoo.edu)
  • You will be redirected to the K login page with your email address pre-populated.  Enter your password and sign in.
  • You will be prompted to use MFA.  Finish the MFA process in the usual way.

Additional Resources 

Get more information about SSO on the Information Services website.
If you have issues with login, please contact the Help Desk at help.desk@kzoo.edu or 269.337.5800.

Cybersecurity Tip: Strong Passwords

Making 50 copies of your house key is probably overkill. Using the same password 50 times is also a bad idea. Use passwords that are strong, long, unique, and random for each site or account. That is the best way to keep your accounts secure.

Learn more at staysafeonline.org

#CybersecurityAwarenessMonth #SecureOurWorld

Cybersecurity Awareness Month – Multi-Factor Authentication

This week’s post for Cybersecurity Awareness Month covers Multi-Factor Authentication.

What is MFA?

An authentication factor is a way for a person to identify oneself to a computer. Multi-Factor Authentication (MFA) means using more than one factor to prove to a computer that you are who you say you are. Typical authentication factors come in three types:

  • Something you know (like a password or PIN number)
  • Something you have (like a phone or ID card)
  • Something you are (biometrics like a fingerprint or facial recognition)

You probably use MFA all the time: when you use an ATM, you use a debit card (something you have) with a PIN (something you know). When someone checks that your face matches the picture on your driver’s license, they’re authenticating you with two factors.

How does MFA help?

According to Microsoft, 99.9% of account compromise attacks can be stopped with MFA. When you use MFA, a cybercriminal who wants to use your account will face a much greater challenge. If your password is compromised but a second authentication factor is required to sign in, a criminal using your password will not be able to authenticate as you. Visit the National Cybersecurity Alliance MFA page for more information.

Where should we use MFA?

You should use MFA with any service that stores sensitive information. These include:

  • financial sites (like your bank, credit card company, or investment account)
  • social media (like Facebook, Instagram, TikTok)
  • email (like Gmail or Hotmail)
  • your Kalamazoo College network account

MFA is required for all students, faculty, and staff, and more information can be found at our Multi-Factor Authentication page.

Subscribe to our Posts

Did you miss the latest IS announcement? Subscribe to receive our posts directly to your inbox!

Cybersecurity Awareness Month – Passwords and Password Manager

This week’s post for Cybersecurity Awareness Month covers habits relating to passwords and password managers. To be cybersecure:

1. Create passwords with these three principles

  • Long – All passwords should be at least 12 characters long.
  • Unique – Never reuse passwords and create unique passwords for each account.
  • Complex – Use a combination of upper and lower case letters, numbers, and special characters.

Remembering passwords and following these principles may sound hard, but there’s a better way…

2. Use a Password Manager

Password managers make it easy to use passwords that are long, unique, and complex. They save time, work across all your devices and operating systems, and can alert you when a password has become compromised. Visit the National Cybersecurity Alliance password managers page for more information including password manager options you can use to be more secure.

3. Know When to Change your Password

As reported by the National Institute of Standards and Technology it is no longer recommended to change your passwords every few months. For personal accounts we recommend focusing on creating long, unique, and complex passwords. Should you become aware that an unauthorized person is accessing an account or a password was compromised in a data breach, change your password immediately. Please note that as part of our process at Kalamazoo College, we require users to change your KNET password periodically; however, there may be a change to this process in the future.

The information on this page was adapted from the National Cybersecurity Alliance’s passwords and NCSAs password manager page.

Subscribe to our Posts

Did you miss the latest IS announcement? Subscribe to receive our posts directly to your inbox!